
Exam Overview
| Exam Code | CSP-Assessor |
| Exam Name | Customer Security Programme Assessor Certification |
| Vendor | Swift |
| Total Questions | 57 |
| Last Updated | 26-Oct, 2026 |
Why CertsPoint?
- Latest & Verified Questions
- Detailed Explanations
- Regular Updates
- Full-Length Practice Tests
- Boost Your Exam Confidence
PDF Study Materials
Downloadable guides and resources
Practice Tests
Full-length tests with real exam experience
Progress Tracking
Monitor your performance and improvement
Study Anywhere
Access on desktop, tablet, and mobile
Secure Payment
Privacy Protected
Money Back Guarantee
Free CSP-Assessor Practice Questions
Explore 4 free practice questions for the Swift CSP-Assessor exam and review the answers and explanations to support your preparation.
-
Question 1
True / FalseCan a Swift user choose to implement the security controls (example: logging and monitoring) in
systems which are not directly in scope of the CSCE? \
-
Option A: TrueCorrect
-
Option B: FalseCorrect
Show Answer & Explanation Hide Answer & Explanation
Correct Answer: A
Explanation
SWIFT Customer Security Programme (CSP) / CSCF-related documents, including:
- Security Controls Policy
- Security Controls Framework v2024
- Independent Assessment Framework
- Assessor Guidelines
- Test Plan Guidelines
- Outsourcing Agents Security Baseline
- CSP Architecture Decision Tree
- Mandatory and Advisory Control Templates
-
-
Question 2
Multiple answersSwift user relies on a sFTP server to connect through an externally exposed connection with a
service provider or a group hub What architecture type is the Swift user? (Choose all that apply.)
-
Option A:Correct
A1
-
Option B:Correct
A2
-
Option C:Correct
A3
-
Option D:Correct
A4
Show Answer & Explanation Hide Answer & Explanation
Correct Answer: B, D
Explanation
-
-
Question 3
Multiple answersApplication Hardening basically applies the following principles. (Choose all that apply.)
-
Option A:Correct
Least Privileges
-
Option B:Correct
Access on a need to have
-
Option C:Correct
Reduced footprint for less potential vulnerabilities
-
Option D:Correct
Enhanced Straight Through Processing
Show Answer & Explanation Hide Answer & Explanation
Correct Answer: A, B, C
Explanation
The correct answers are A. Least Privileges, B. Access on a Need-to-Have Basis, and C. Reduced Footprint for Less Potential Vulnerabilities.
Application Hardening is the process of securing applications by minimizing their attack surface and reducing security risks. It follows the principle of least privilege, which ensures that users, processes, and applications are granted only the minimum permissions required to perform their functions. It also enforces access on a need-to-have basis, meaning access rights are provided only when necessary for business or operational purposes. Another key principle is maintaining a reduced footprint, which involves disabling or removing unnecessary services, features, accounts, and software components to decrease the number of potential vulnerabilities that attackers could exploit. Enhanced Straight Through Processing (STP) is related to improving the efficiency of transaction processing and automation, not to application hardening or security strengthening. Therefore, A, B, and C are the correct answers. -
-
Question 4
Multiple answersUsing the outsourcing agent diagram. Which components must be placed in a secure zone? (Choose
all that apply.)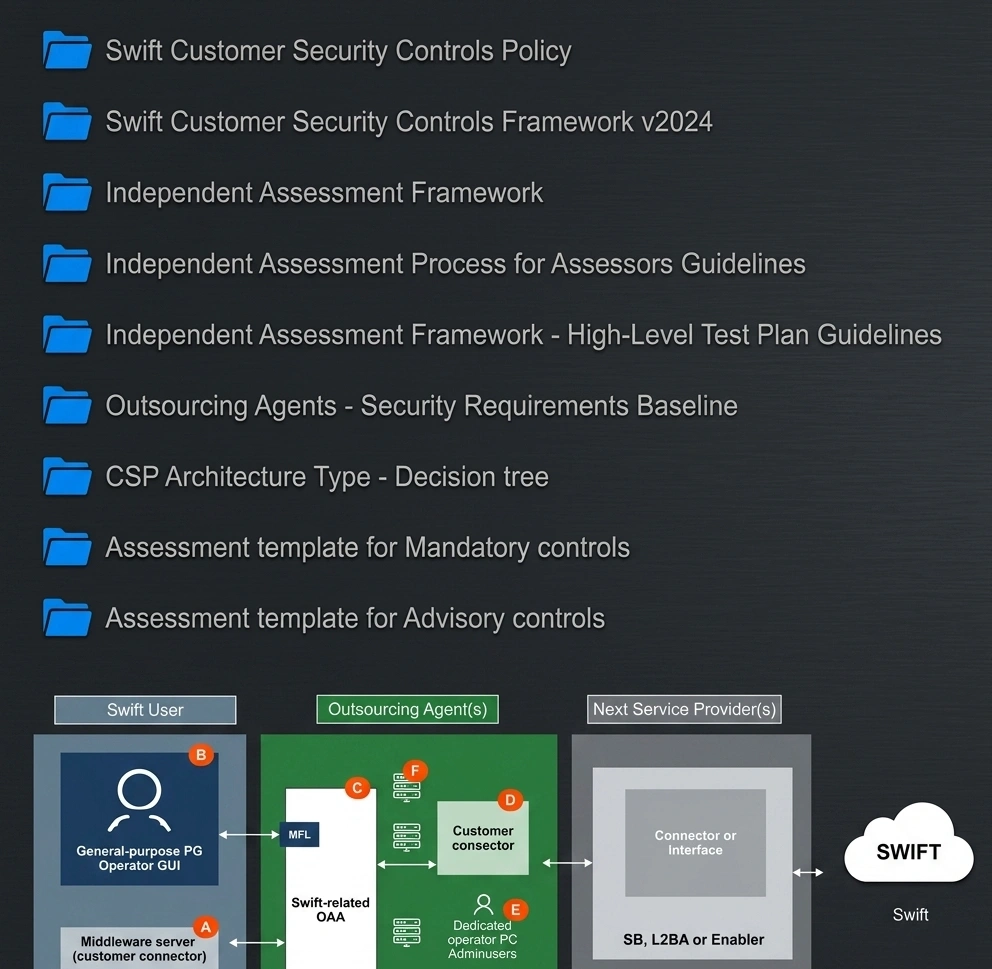
-
Option A:Correct
Component A
-
Option B:Correct
Component B
-
Option C:Correct
Component C
-
Option D:Correct
Component D
Show Answer & Explanation Hide Answer & Explanation
Correct Answer: A, D
Explanation
-